GRC Tool

Audit evidence that already exists when the auditor asks.

One register for your obligations, controls, policies, risks and incidents, so compliance runs all year instead of the week before an audit.

For risk, compliance and internal audit teams in regulated institutions

Control libraryRisk registerAudit evidence
From

Controls in spreadsheets, evidence gathered by hand each audit

To

One living register, with evidence ready on demand

What we offer

Glass regulation sheets linked by rods to glass shields; the front shield glows red with a tick
How we work
  1. Gather the obligations you report against
  2. Map each one to controls, owners and tests
  3. Schedule testing and attestation
01

Obligations & Control Library

Every regulation mapped to a control, an owner and a test.

The challenge

Regulations change, controls live in different files, and nobody can say for certain which control answers which obligation.

What you receive
  • Control library mapped to obligations
  • Policy lifecycle with attestation
  • Testing schedule and reminders
The outcome

A clear line from every obligation to the control that meets it.
  1. Glass regulation sheets linked by rods to glass shields; the front shield glows red with a tick
    01 / 03

    Obligations & Control Library

    Every regulation mapped to a control, an owner and a test.

    The challenge

    Regulations change, controls live in different files, and nobody can say for certain which control answers which obligation.

    How we work
    1. Gather the obligations you report against
    2. Map each one to controls, owners and tests
    3. Schedule testing and attestation
    What you receive
    • Control library mapped to obligations
    • Policy lifecycle with attestation
    • Testing schedule and reminders
    The outcome

    A clear line from every obligation to the control that meets it.

  2. A glass heat-map grid of tiles at different heights; the tallest tile glows red beside its owner
    02 / 03

    Risk Register & Incidents

    Risks with owners, treatments and a history.

    The challenge

    Risks are listed once a year and forgotten, and incidents live in email threads that nobody can search.

    How we work
    1. Set up your risk taxonomy and scoring
    2. Capture risks and incidents with owners
    3. Track treatment plans to closure
    What you receive
    • Risk register with treatment tracking
    • Incident logging and root-cause records
    • Heat maps and trend views
    The outcome

    Risks that are managed, not just recorded.

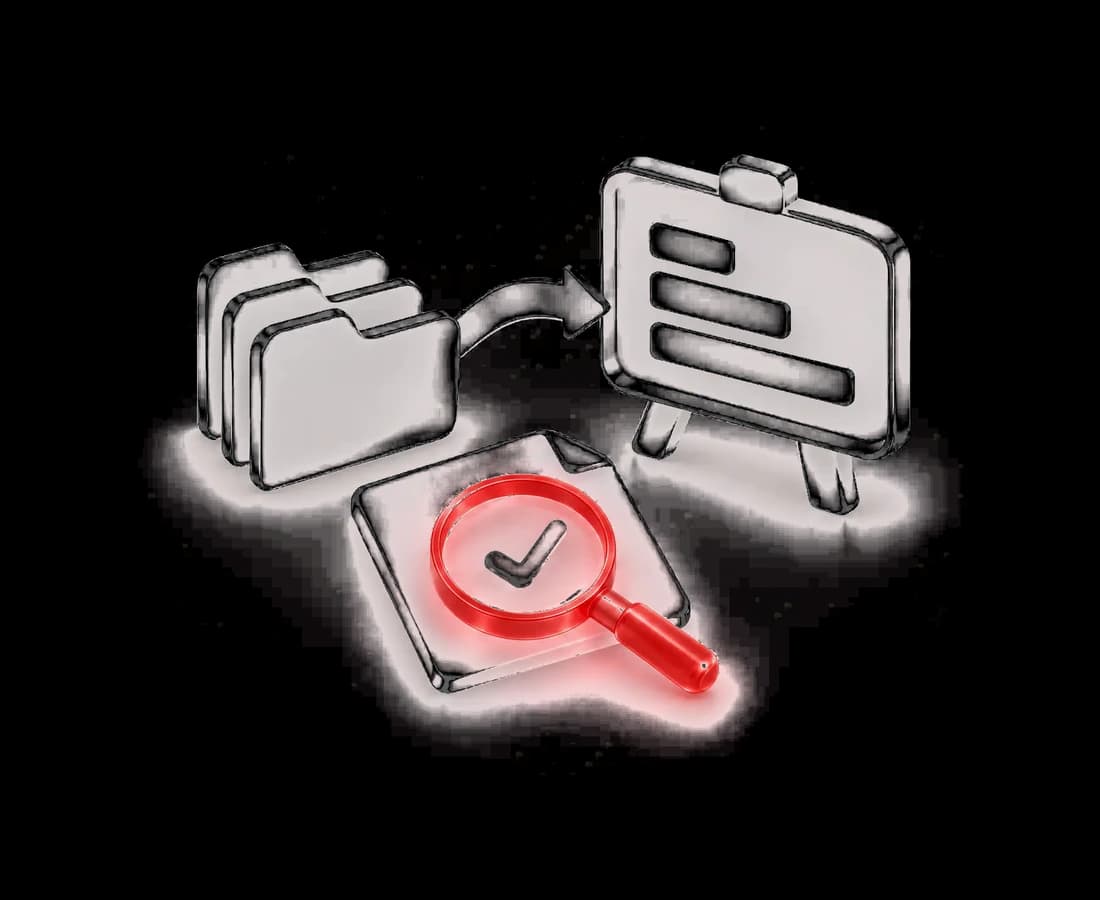
  3. Glass folders feed a presentation board; a red magnifier rests on a ticked document
    03 / 03

    Audit & Board Reporting

    Evidence gathered as work happens.

    The challenge

    Every audit cycle, teams rebuild the evidence pack by hand and the board sees a picture weeks out of date.

    How we work
    1. Link evidence to controls as tests run
    2. Manage audit findings and actions
    3. Report status to management and the board
    What you receive
    • Audit evidence and findings management
    • Board and regulator reporting packs
    • Full audit trail on every change
    The outcome

    Audits that check the work, rather than wait for it.

How an engagement runs

First control set live, then the rest.

  1. Scope

    The obligations and business units that matter most.

  2. Configure

    Taxonomies, workflows and roles set up in the platform.

  3. Load

    Your first control set, risks and policies mapped and loaded.

  4. Embed

    Owners trained, first attestation cycle run with you.

AI governance included

AI creates obligations of its own.

Model inventory, human oversight and audit trails for AI belong in the same register as the rest of your controls. We set them up alongside.

  • Model and AI system inventory
  • Human-oversight controls
  • Data Protection Act obligations
  • Audit trail on every change

Stop rebuilding the evidence pack.

See your own obligations mapped to controls in a 30-minute walkthrough with our GRC team.