VAPT & Security Services

Find the weak points before attackers do.

Vulnerability scanning and expert-led penetration testing across your networks, applications and APIs, with a clear plan to fix what we find.

For institutions that hold customer data, move money or answer to a regulator

Vulnerability scanningPenetration testingRemediation reports
From

Security tested rarely, weaknesses found by attackers

To

Regular testing, prioritised fixes, evidence for the regulator

What we offer

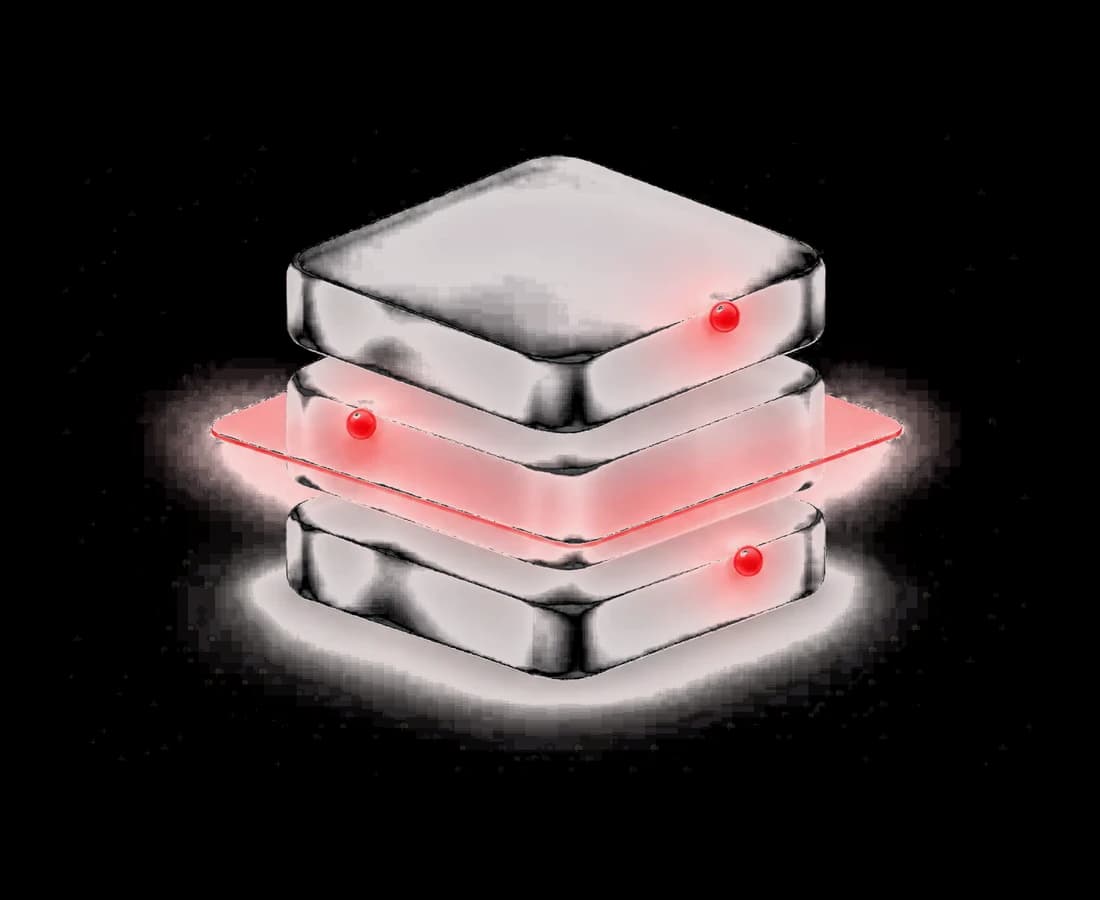
A scanning plane passes through a glass server stack; red dots mark weak points
How we work
  1. Agree scope and rules of engagement
  2. Scan networks, systems and applications
  3. Validate findings to remove false alarms
01

Vulnerability Assessment

Systematic scanning of every layer.

The challenge

Unpatched software and weak configurations leave easy entry points that nobody has seen.

What you receive
  • Network, system and application scanning
  • Configuration and patch reviews
  • Validated list of exposures
The outcome

A complete picture of where you are exposed.
  1. A scanning plane passes through a glass server stack; red dots mark weak points
    01 / 03

    Vulnerability Assessment

    Systematic scanning of every layer.

    The challenge

    Unpatched software and weak configurations leave easy entry points that nobody has seen.

    How we work
    1. Agree scope and rules of engagement
    2. Scan networks, systems and applications
    3. Validate findings to remove false alarms
    What you receive
    • Network, system and application scanning
    • Configuration and patch reviews
    • Validated list of exposures
    The outcome

    A complete picture of where you are exposed.

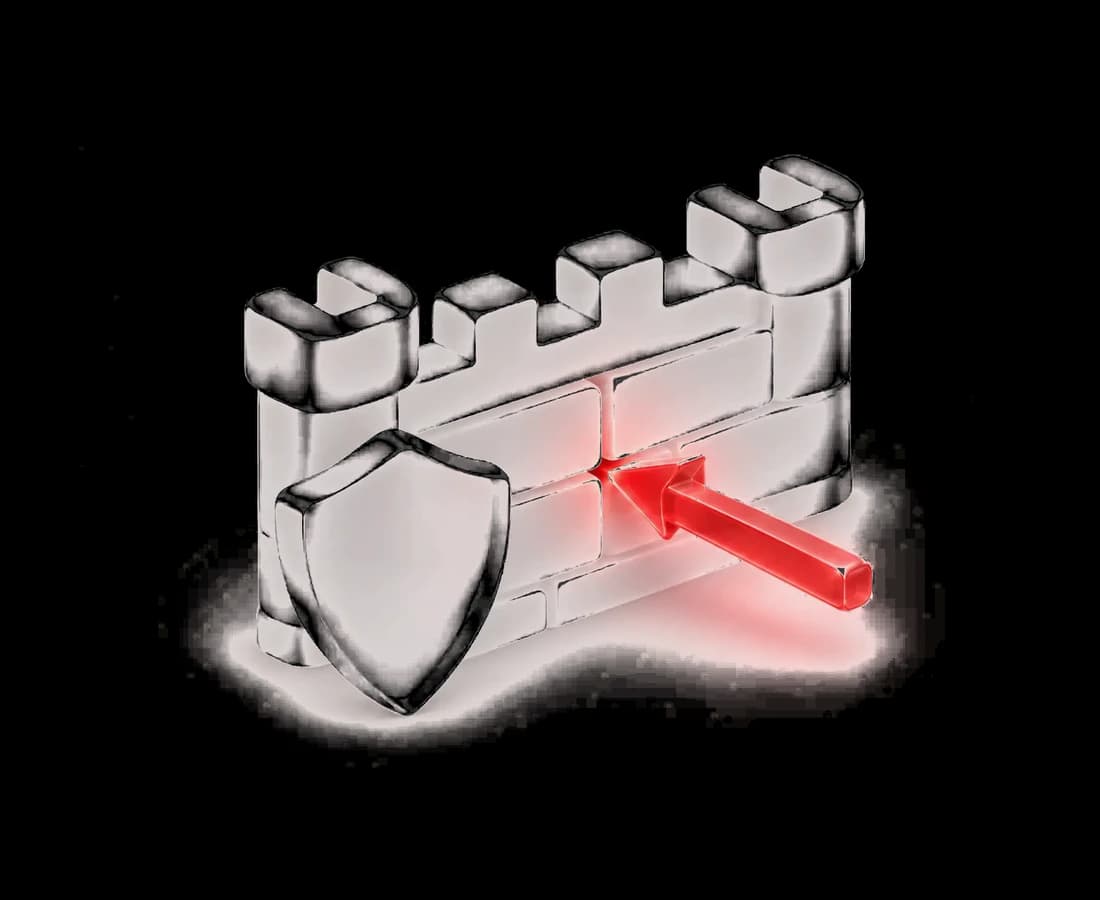
  2. A red arrow probes a gap in a glass fortress wall behind a shield
    02 / 03

    Penetration Testing

    Simulated attacks, run by experts.

    The challenge

    Automated scans miss what a determined attacker would chain together to get in.

    How we work
    1. Model the attacks that matter to your business
    2. Test web, API, mobile and infrastructure targets
    3. Show how each weakness could be exploited
    What you receive
    • Web, API and mobile application testing
    • Internal and external infrastructure testing
    • Proof of exploitability for each finding
    The outcome

    You see your systems the way an attacker would.

  3. A glass report inside a loop arrow, closed by a red tick, with a wrench beside it
    03 / 03

    Reporting & Re-testing

    Prioritised, step by step, then checked.

    The challenge

    Long reports without priorities leave teams unsure what to fix first.

    How we work
    1. Rank findings by risk and business impact
    2. Give step-by-step remediation guidance
    3. Re-test and confirm each fix
    What you receive
    • Executive summary and risk rating
    • Detailed remediation guidance
    • Re-test results for your auditors
    The outcome

    Fewer open risks, and evidence that they are closed.

How an engagement runs

Scoped, tested, reported, re-tested.

  1. Scope

    Targets, timing and rules agreed in writing.

  2. Assess

    Scanning and configuration review.

  3. Attack

    Expert-led penetration testing.

  4. Fix & re-test

    Prioritised report, then confirmation of every fix.

Standards

Testing aligned to the frameworks your auditors use.

Findings are mapped to recognised standards, and any data in scope is covered by a data-processing agreement. Testing AI systems too? See Automated Offensive Security.

  • OWASP Top 10 for web and API
  • Rules of engagement in writing
  • Data-processing agreement
  • Re-test attestation on close-out

Test it before someone else does.

Tell us what you need tested and we will come back with a scope, a timeline and rules of engagement.